Infrastructure
A network built for real traffic.
Hexado runs from the TTC datacenter in Prague, Czechia on our own network layer under AS210436. We operate routing, public addresses, protection and monitoring so VPS, game servers and dedicated machines are more than a line in a spec sheet.
Datacenter
TTC in Prague, Czechia
Autonomous system
AS210436
Ports
10 Gbps
Protection
GSL
AS210436
Own routing and clear responsibility.
Public services are routed through our own autonomous system. That gives us control over address space, traffic rules and how services behave during peaks or attacks.
Routing
Hexado edge
Anti-DDoS administration
Enterprise clients can see attacks, subnets and mitigations in one place.
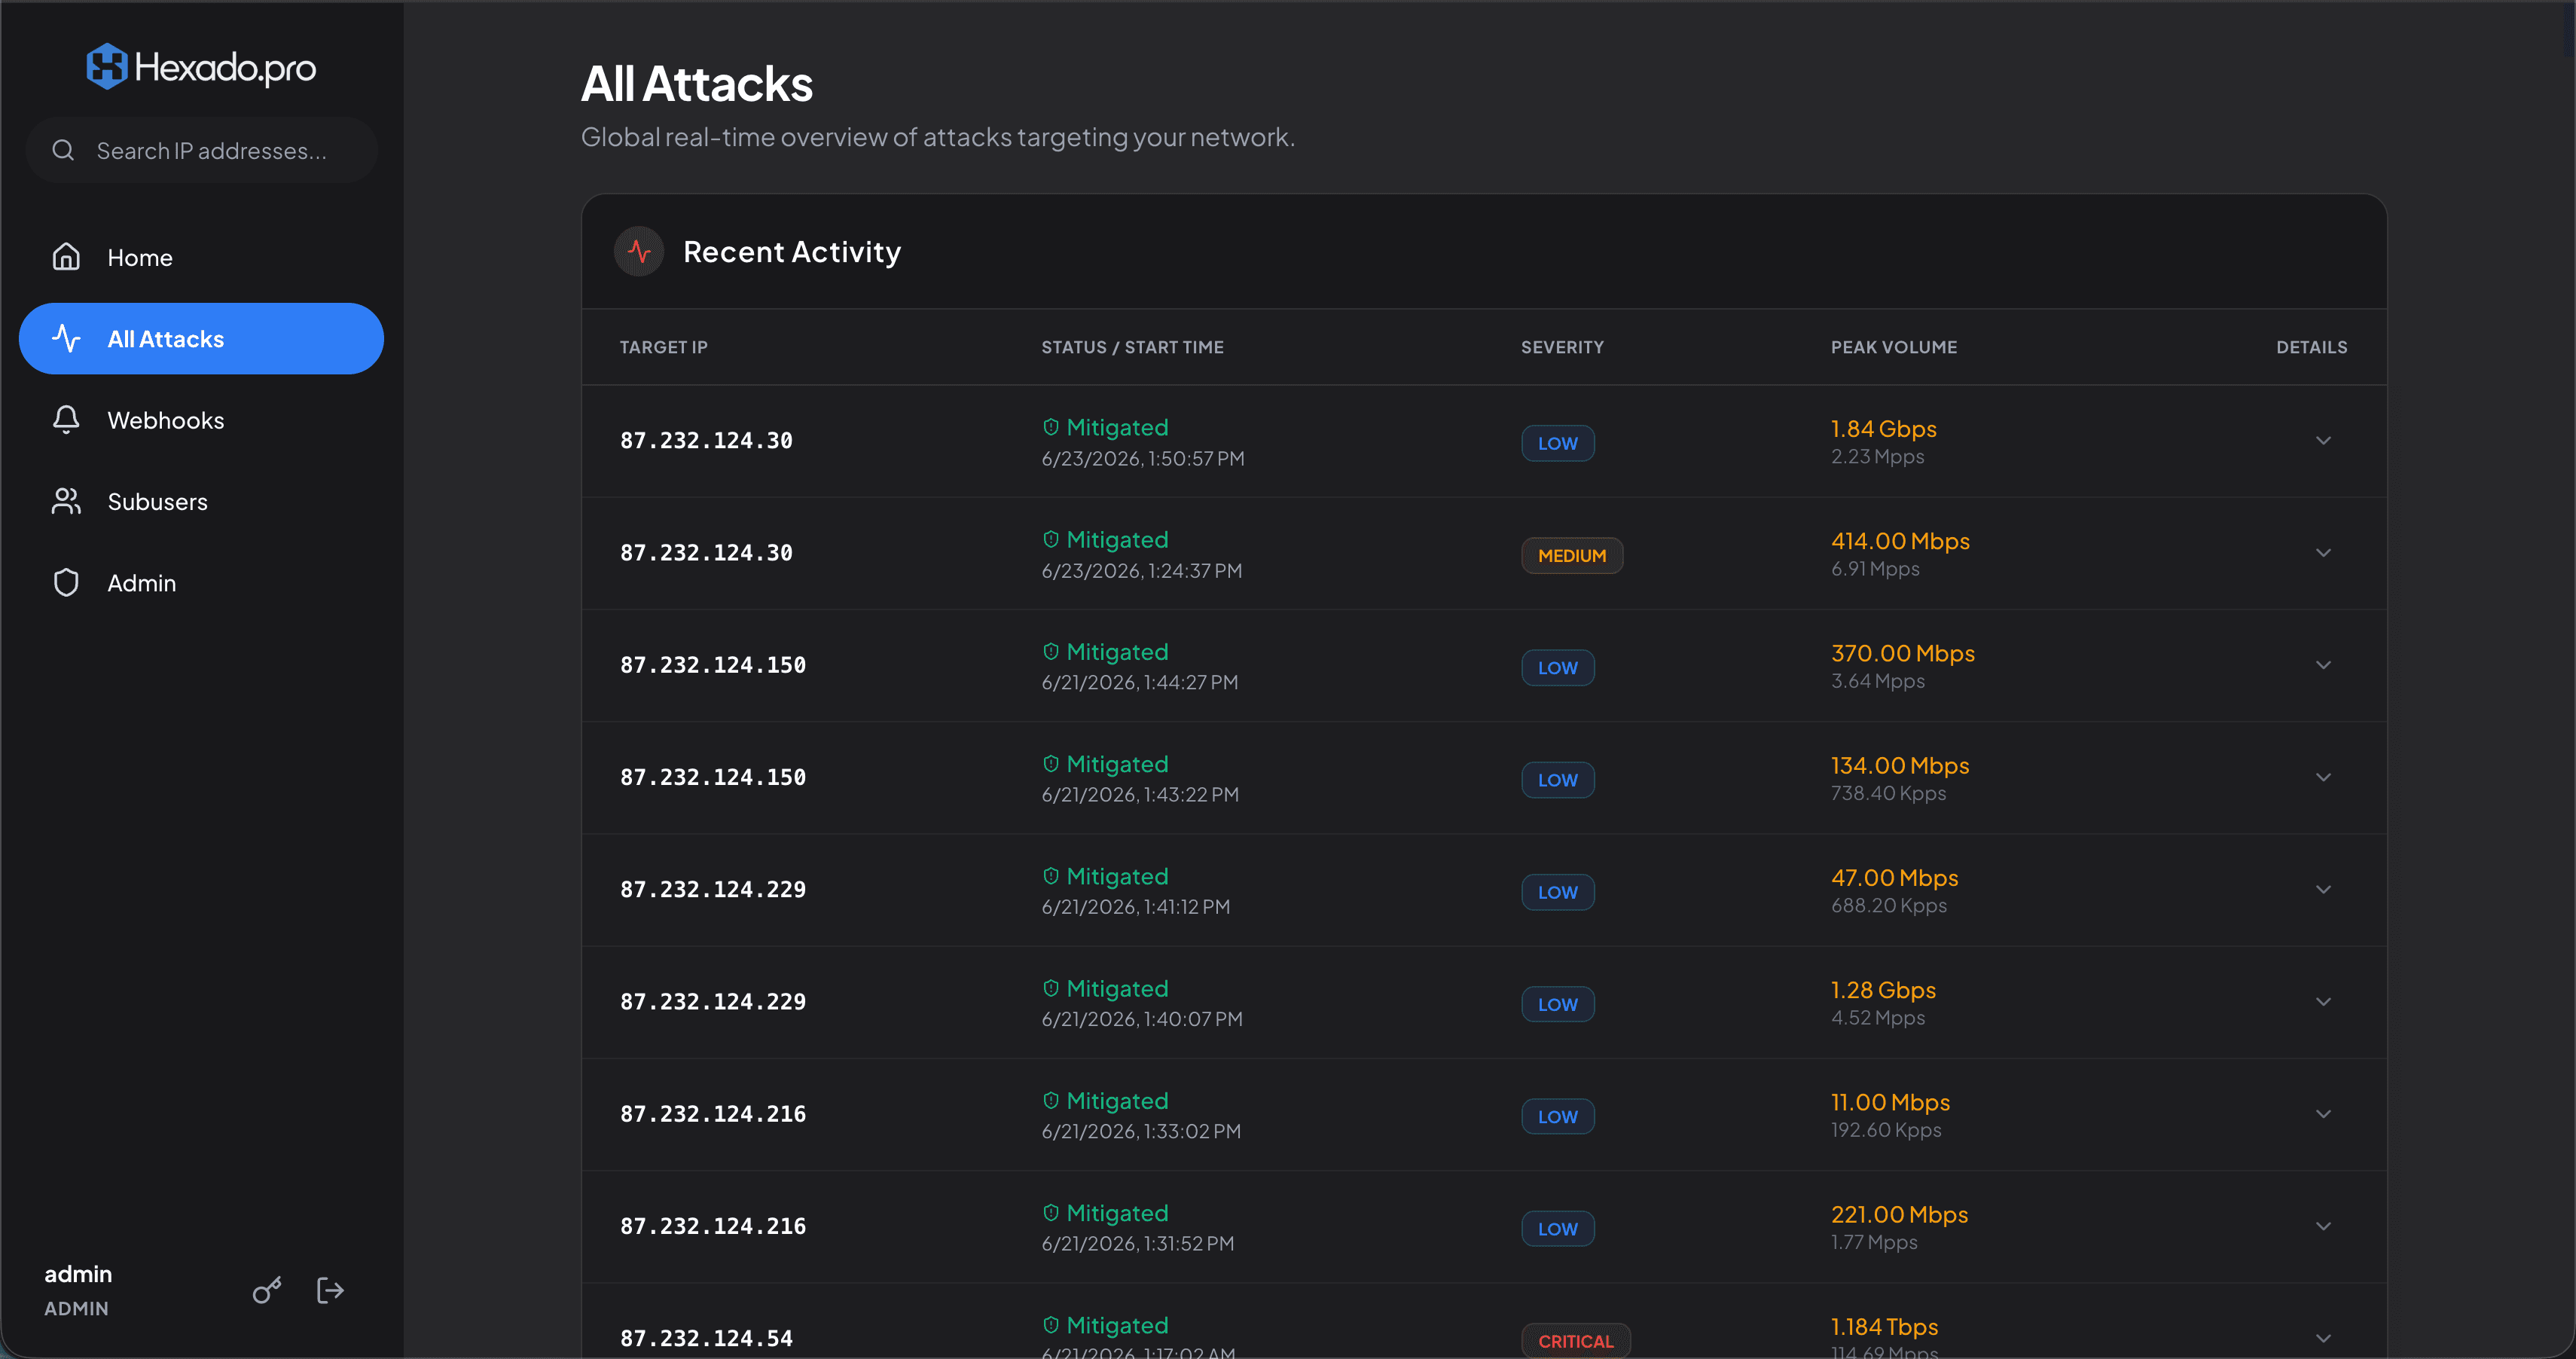
For demanding public workloads, we provide our own Anti-DDoS administration. It shows current and historical attacks, target IP addresses, severity, peak volume and mitigation status. It is built for clients who need visibility, not only background protection.
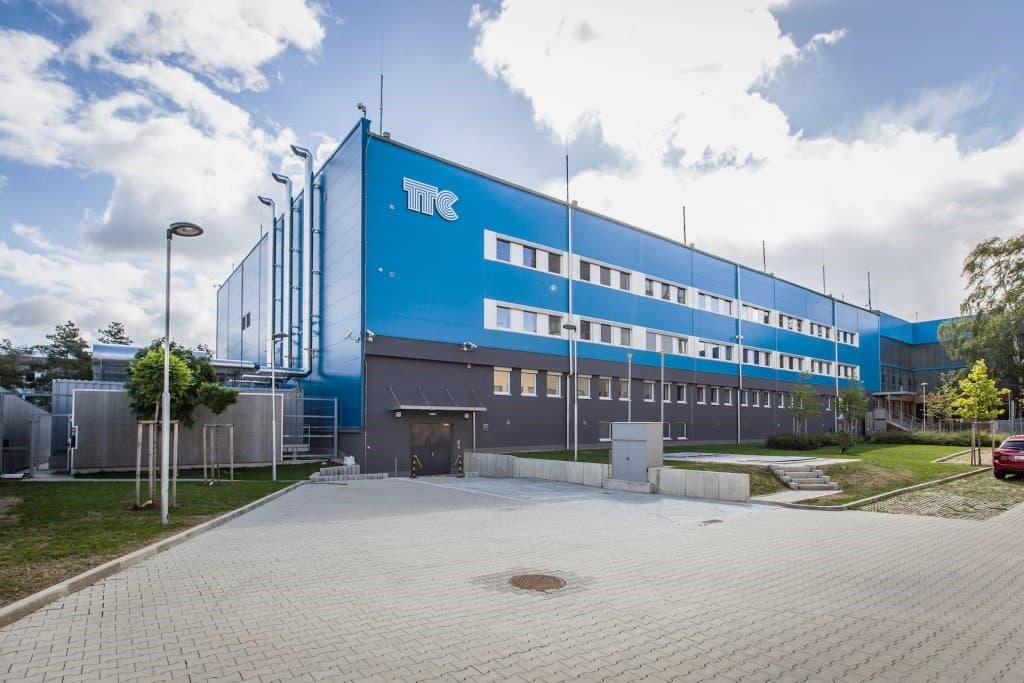

TTC datacenter · Prague, Czechia
Physical base in TTC in Prague, Czechia. Operational layer by Hexado.
TTC in Prague, Czechia provides the datacenter foundation: power, cooling and physical availability. Hexado operates the network logic above it: routing, public subnets, protection rules, monitoring and server operations.
Hexado operations
What Hexado operates directly
01
Addresses and subnets
Public IPv4 addresses run under our AS210436, so we can plan them around the service instead of a fixed template.
02
Traffic protection
We combine Global Secure Layer inline filtering, L3/L4 and L7 rules, plus our own mitigation overview for demanding clients.
03
Operational monitoring
We care how the service behaves during peaks, attacks or growth. Not only whether a server shows green.
Need stable public infrastructure?
Send us the service type, expected traffic and critical parts of the project. We will suggest a sensible base from VPS to dedicated infrastructure.