Always-on protection
Filtering stays active without manual activation during an attack.
Anti-DDoS · Global Secure Layer
We protect public IP addresses, game servers, APIs, websites and dedicated infrastructure. We combine L3/L4 and L7 protection, Global Secure Layer inline mitigation, our own AS210436 network and a clear administration panel for enterprise clients.
Protection
GSL
Layers
L3 / L4 / L7
Network
AS210436
Datacenter
TTC in Prague, Czechia
Enterprise panel
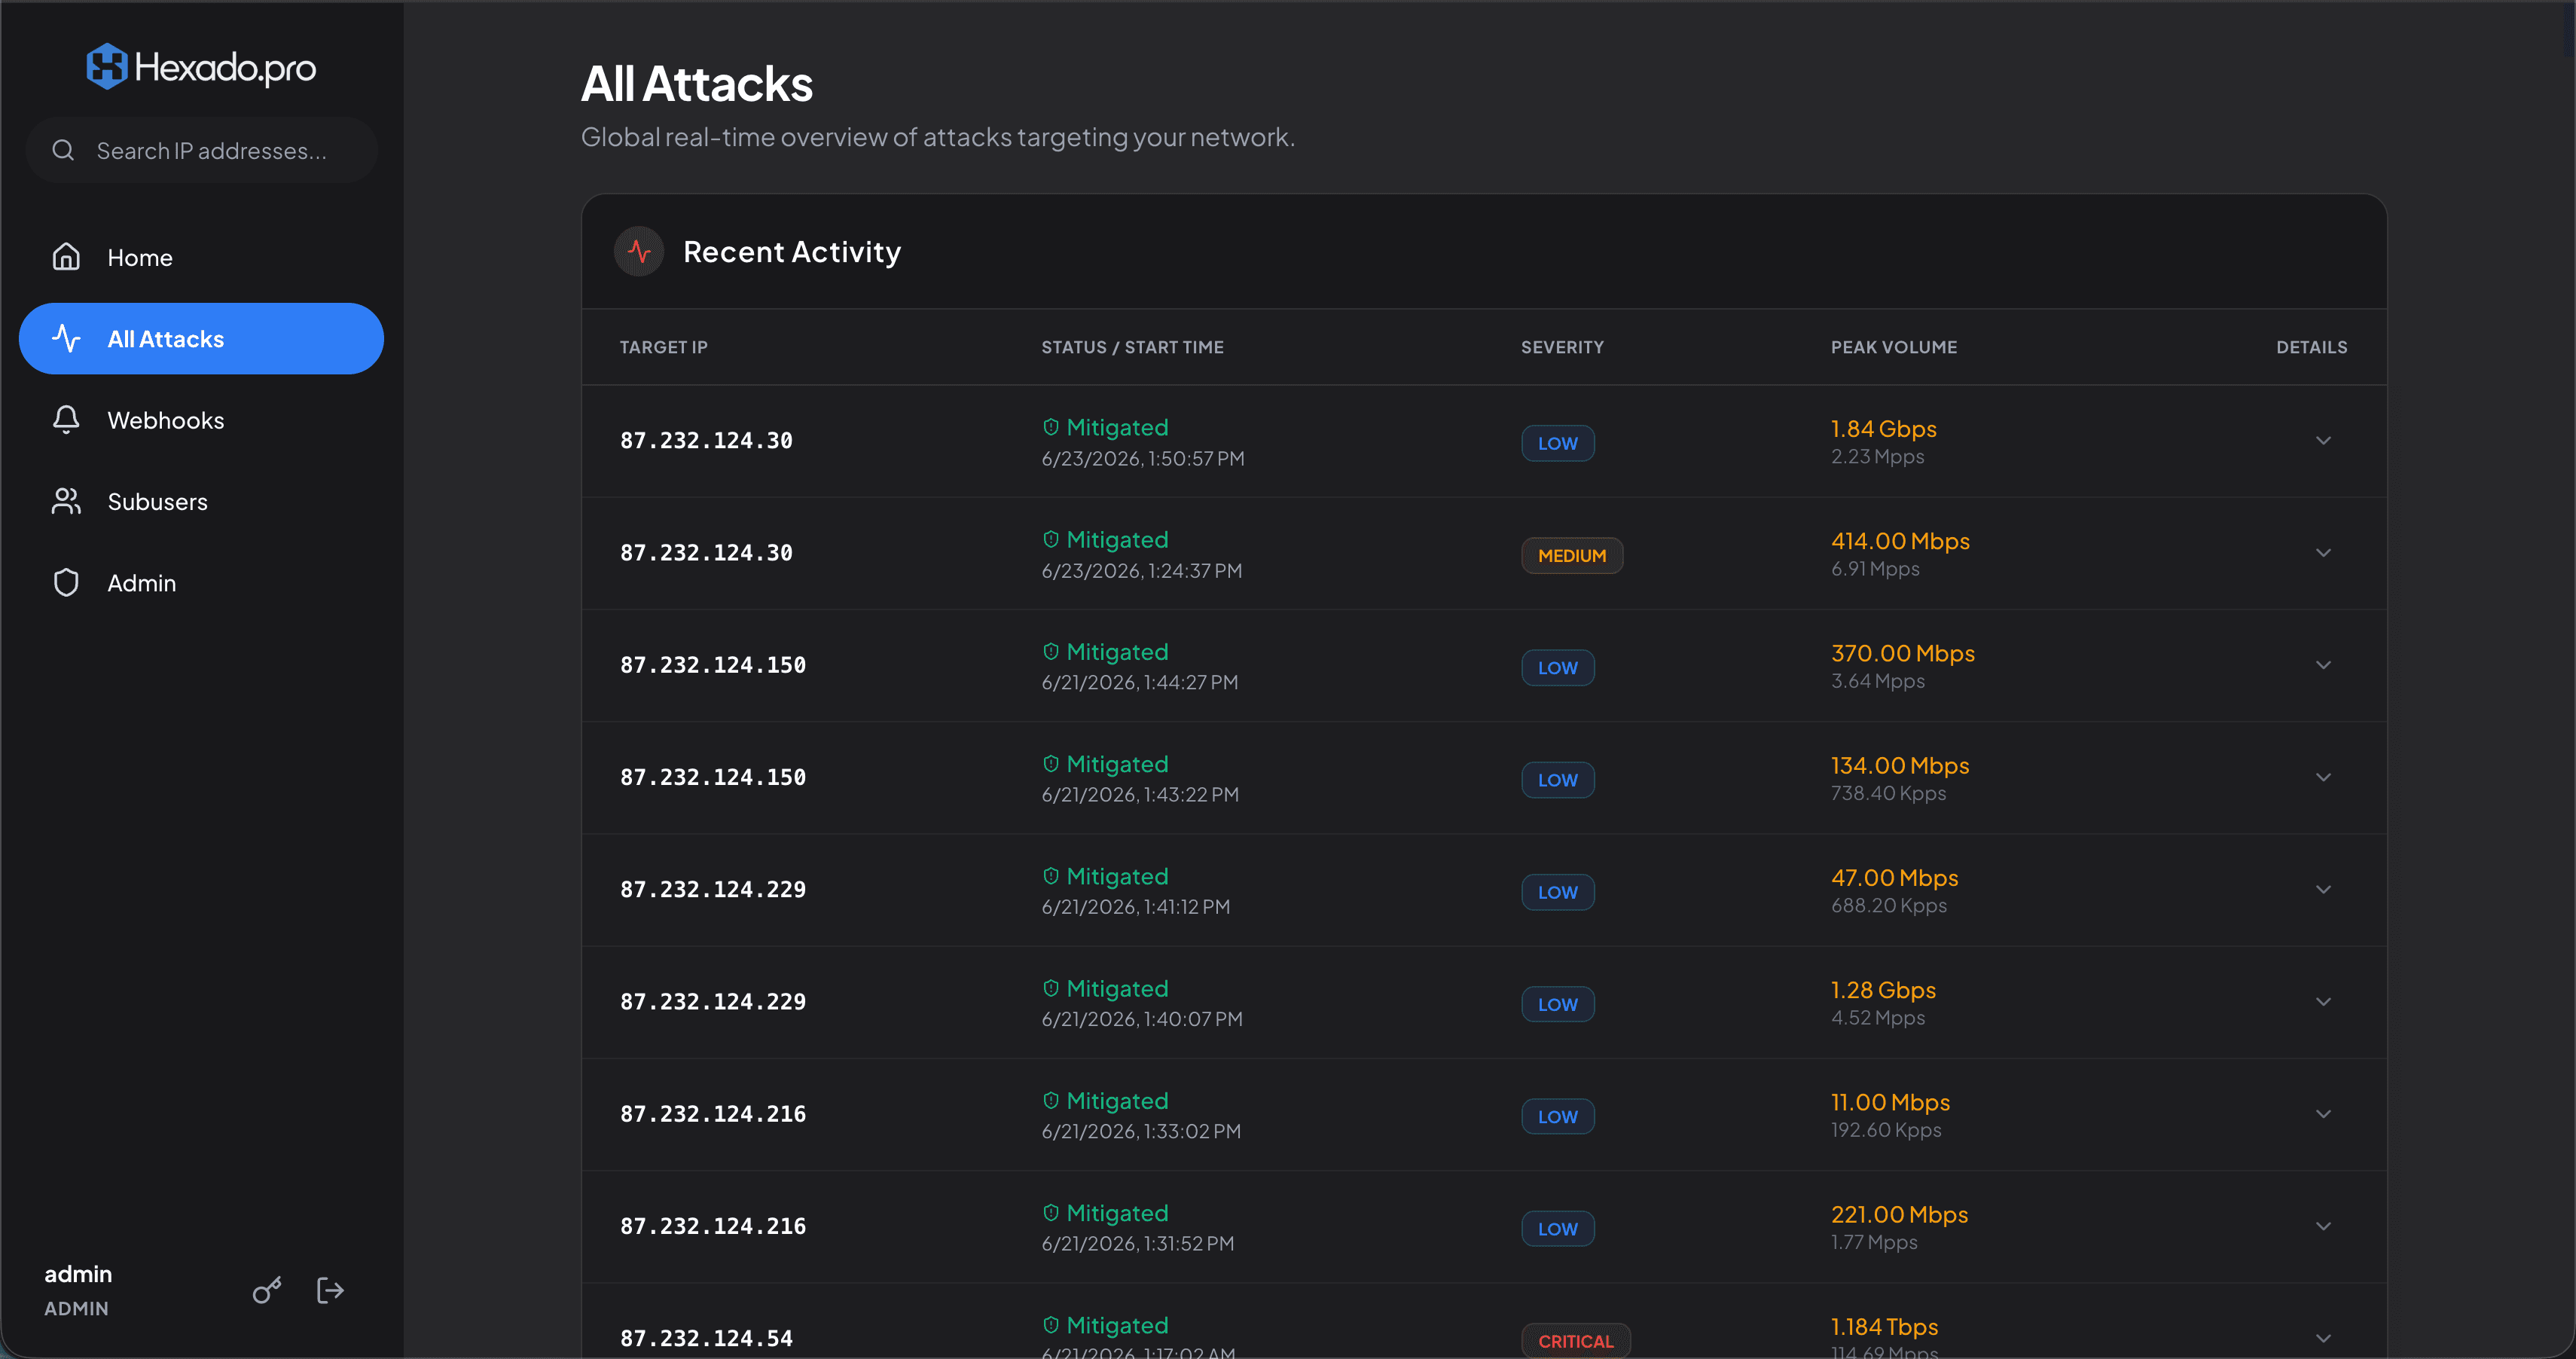
For demanding clients, simply saying that protection is enabled is not enough. Our Anti-DDoS administration shows target IP addresses, mitigation status, severity, peak volume and incident history. It is useful for public services, communities, game servers and workloads with their own subnet.
How traffic is protected
Always-on inline filtering, global Anycast and automated mitigation. GSL removes attacks at the network edge; our servers run at TTC in Prague, Czechia.
Global Secure LayerFiltering stays active without manual activation during an attack.
Malicious traffic is filtered close to its source.
Detection and response run in real time.
We tune protection around ports and traffic.
Infrastruktura
Anti-DDoS is not a separate box next to a server. It connects to routing, the TTC datacenter in Prague, Czechia, public addresses under AS210436 and the way traffic reaches your services.
More about infrastructure01
Minecraft, FiveM, CS2, voice servers and public community projects.
02
HTTP/S traffic, logins, checkout, admin areas and sensitive endpoints.
03
Public IP addresses, custom stacks, databases and production services.
04
Larger address ranges where visibility and clear traffic rules matter.
FAQ
Short answers to the points that usually matter before deploying protection.
Yes. We do not rely only on raw L3/L4 capacity, we also use L7 rules for websites, APIs and sensitive services.
For public services, protection is considered from the start. The exact setup depends on traffic, ports and IP scope.
Yes. Larger projects can run with subnet-level protection and custom rules under our AS210436 network.
Servers are located at TTC in Prague, Czechia. Global Secure Layer protects traffic across its global network before delivery to our AS210436 network.
Send us the traffic type, ports, expected load and whether you need protection for one IP or a whole subnet. We will suggest a setup that fits your traffic.